Bidang
Keamanan Siber
Istilah keamanan yang wajib diketahui setiap bisnis: phishing, ransomware, enkripsi, autentikasi dua faktor, zero trust, backup dan kebiasaan yang menjaga data serta akun tetap aman.
35 konsep di bidang ini
Keamanan Siber
T
Two-Factor Authentication 2FA Two-factor authentication is a sign-in that asks for your password and then for something you are holding, so a stolen password alone is not enough to get in. Baca definisinya
P
Phishing Phishing is a message built to look like it came from someone you trust, so that you hand over a password, a code or a payment. Baca definisinya Password Manager A password manager is a small program that remembers every password for you and keeps them locked away, leaving you just one to memorise. Baca definisinya
A
Authenticator App An authenticator app is a free app on your phone that produces the six-digit code a website asks for after your password, so a stolen password is not enough. Baca definisinya
S
SIM Swap Fraud SIM swap fraud is a scam in which a criminal moves your phone number onto their own SIM card, so your calls and security codes reach them instead. Baca definisinya Social Engineering Social engineering is an attack on the person rather than the computer, where someone uses fear or hurry to talk you into handing over a code or a payment. Baca definisinya
I
Invoice Fraud Invoice fraud is a fake or altered supplier bill that gets you to pay a real amount into a bank account the criminal controls. Baca definisinya
Q
QR Code Phishing (Quishing) QR code phishing, also called quishing, is a scam where a fake code is stuck over a real one so your phone opens a fake payment page. Baca definisinya
S
Security Awareness Training Security awareness training is the short, regular practice that teaches your staff to spot a fake email or phone call before they act on it. Baca definisinya
M
Malware Malware is any program written to damage your computer or to work quietly for someone else while you carry on using it. Baca definisinya
R
Ransomware Ransomware is a program that locks every file on a company's computers and then demands a payment before it will hand them back. Baca definisinya
K
Keylogger A keylogger is a hidden program that records every key someone types on a computer, including the password to the company bank account. Baca definisinya
B
Backup A backup is a second copy of your files, kept somewhere safe from whatever destroys the first copy, so you can get your work back. Baca definisinya
D
Disaster Recovery Plan DRP A disaster recovery plan is a short written document that says exactly what your business does, and who does it, on the morning the systems stop working. Baca definisinya
L
Least Privilege Least privilege means each person can open only the screens their own job needs, so a stolen account cannot reach the rest of the business. Baca definisinya
U
User Access Review A user access review is a regular check of who can still log into your systems, including the accounts nobody remembers creating. Baca definisinya
O
Offboarding Offboarding is the security work a business does when someone leaves, closing every login and shared password they had so nothing stays open behind them. Baca definisinya
Z
Zero Trust Zero trust is a way of working where nobody is trusted just for sitting inside the office, and every single login is checked again. Baca definisinya
P
Patch Management Patch management is the habit of updating every program and device you use on a set plan instead of whenever someone remembers. Baca definisinya
E
End-of-Life Software EOL End-of-life software is a program its maker has stopped repairing, so any weakness someone finds in it from that day on stays open forever. Baca definisinya Ethical Hacking Ethical hacking is an attack on your own system that you asked for and paid for, so a trusted expert finds the holes before a criminal does. Baca definisinya
W
Web Application Firewall WAF A web application firewall is a filter that reads every request arriving at your website and blocks the ones that look like a known attack. Baca definisinya
O
OWASP Top 10 The OWASP Top 10 is a free list of the ten mistakes that most often let a stranger into a website or a web application. Baca definisinya
J
Jailbroken Device A jailbroken device is a phone whose built-in protections have been removed on purpose, which lets one app read what another app keeps private. Baca definisinya
T
Third-Party Risk Third-party risk is the chance that your data leaks through a supplier, a freelancer or a plugin you trusted, rather than through your own team. Baca definisinya
E
Encryption Encryption is a way of scrambling your information into nonsense, so that only the person holding the right key can read it again. Baca definisinya
H
HTTPS HTTPS is the protected version of a web address, and it scrambles everything sent between a visitor's browser and your site so nobody in between can read it. Baca definisinya
P
PCI Compliance PCI DSS PCI compliance is the set of safety rules that the card companies make every business follow before it is allowed to take card payments. Baca definisinya
D
Data Breach A data breach is the moment private customer information leaves your control, whether a thief took it or someone simply sent it to the wrong address. Baca definisinya
C
Cyber Insurance Cyber insurance is a policy that pays for the clean-up after an attack, as long as you kept the security promises you made on the application form. Baca definisinya
G
GDPR GDPR GDPR is the European law that sets out how a business may collect, keep and use the personal information of the people it serves. Baca definisinya
V
Vulnerability Scan A vulnerability scan is an automatic check that searches a website or an app for weaknesses attackers already know about and reports what it finds. Baca definisinya Virtual Private Network VPN A virtual private network is a sealed tunnel through a public connection, so what your staff send on café or hotel wifi cannot be read by anyone nearby. Baca definisinya
Z
Zero-Day Vulnerability A zero-day vulnerability is a hole in software that has just been found and has no fix yet, so everyone using that part is exposed until one arrives. Baca definisinya
S
SQL Injection SQLi Serangan web ketika seseorang mengetik perintah database di formulir atau alamat web, lalu situs menjalankannya sehingga data yang seharusnya dilindungi bisa terlihat, berubah, atau terhapus. Baca definisinya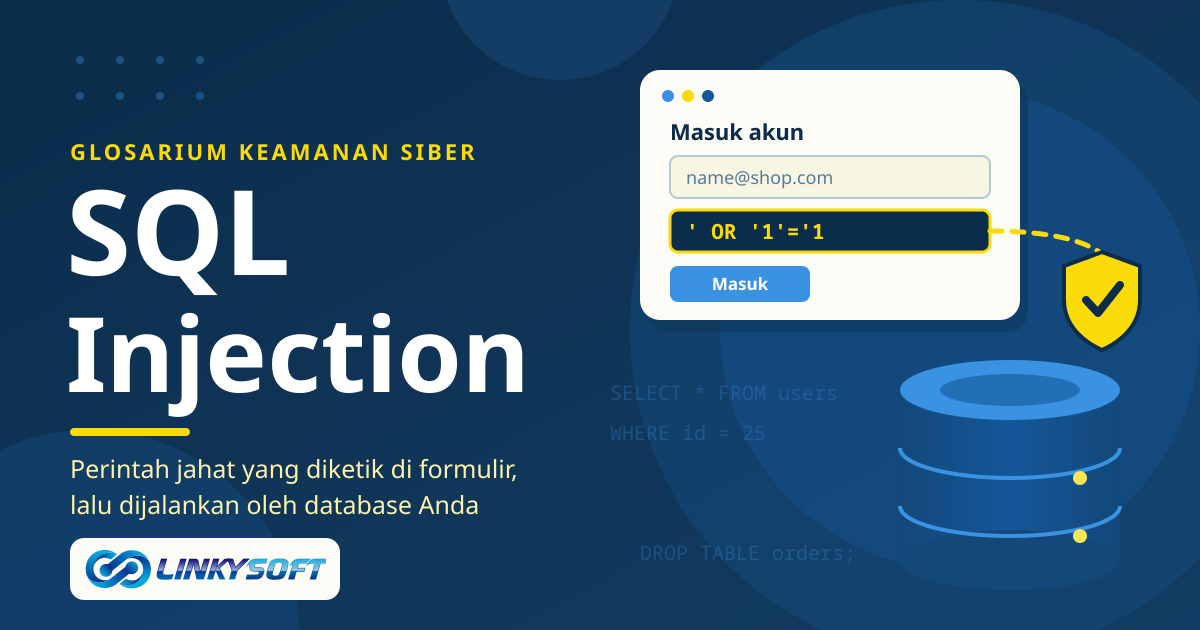
Bidang lainnya
Web Hosting Definisi sederhana istilah web hosting yang Anda temui saat membuat website online: uptime, perjanjian tingkat layanan, penyimpanan, SSL dan bagian paket hosting yang menentukan seberapa cepat dan andal sebuah situs. 2 Server Fungsi server dan database di dalamnya dengan bahasa sederhana: VPS dan server dedicated, MySQL, PostgreSQL, MongoDB, Redis serta istilah yang Anda perlukan saat mengelola server sendiri. 4 Domain Nama domain dibuat sederhana: pendaftaran, DNS, nameserver, perpanjangan, transfer dan istilah yang Anda perlukan untuk memilih, menghubungkan dan melindungi alamat website Anda. 0 E-commerce Bahasa jualan online: SKU, varian produk, keranjang yang ditinggalkan, pelacakan pesanan, pembayaran, kasir (point of sale) dan angka yang menunjukkan kondisi toko sebenarnya. 30 Cloud Computing Cloud computing dan alat untuk mengirim software ke sana: apa itu cloud, bagaimana Docker dan Kubernetes menjalankan aplikasi, serta bagaimana Git dan CI/CD menjaga setiap rilis tetap aman. 5 Media Sosial Istilah media sosial untuk bisnis: pemasaran lewat WhatsApp, kampanye influencer, iklan video dan istilah di balik menumbuhkan audiens serta menyapa pelanggan di tempat mereka berada. 3 Website Komponen dasar sebuah website dengan bahasa sederhana: HTML, CSS, desain responsif, tata letak kanan ke kiri dan perbedaan website dengan aplikasi web. 6 Aplikasi Web Istilah yang Anda temui saat perusahaan membangun atau membeli aplikasi web: API, dashboard, peran pengguna, single sign-on, deployment, skalabilitas dan biaya memiliki software. 29 Aplikasi Mobile Istilah aplikasi mobile dijelaskan: aplikasi native dan hybrid, notifikasi push, pembelian dalam aplikasi, review app store, sinkronisasi offline dan apa yang menjaga aplikasi tetap terbaru dan aman. 25 Digital Marketing Istilah digital marketing dijelaskan: conversion rate, landing page, sales funnel, kampanye email, pay per click, atribusi dan angka yang menunjukkan apa yang benar-benar berhasil. 26 Kecerdasan Buatan Kecerdasan buatan dengan bahasa sederhana: machine learning, large language model, chatbot dan cara bisnis memakai AI untuk menjawab pelanggan serta mengotomatiskan pekerjaan sehari-hari. 4 Internet of Things Istilah Internet of Things dibuat sederhana: perangkat terhubung, sensor, gateway dan istilah di balik gedung pintar, pelacakan dan mesin yang melaporkan statusnya sendiri. 0 Bahasa Pemrograman Definisi singkat dan jelas bahasa pemrograman di balik software masa kini: Python, PHP, JavaScript, TypeScript, Java, Go, Rust, Kotlin, Swift, SQL dan lainnya. 12 Framework Framework yang dipakai developer, didefinisikan dengan jelas: Laravel, Django, React, Next.js, Node.js, Flutter dan apa yang dibawa masing-masing ke proyek web atau mobile. 6 Mesin Pencari Istilah mesin pencari dijelaskan: SEO, indexing, sitemap, URL kanonis, featured snippet, search intent dan apa yang membantu website muncul di Google dan jawaban AI. 30 Antarmuka Pengguna Istilah antarmuka dan pengalaman pengguna: prototipe, user experience, mode gelap dan pilihan desain yang membuat software dan website mudah serta nyaman dipakai. 3